Rules-based fraud detection in SQL
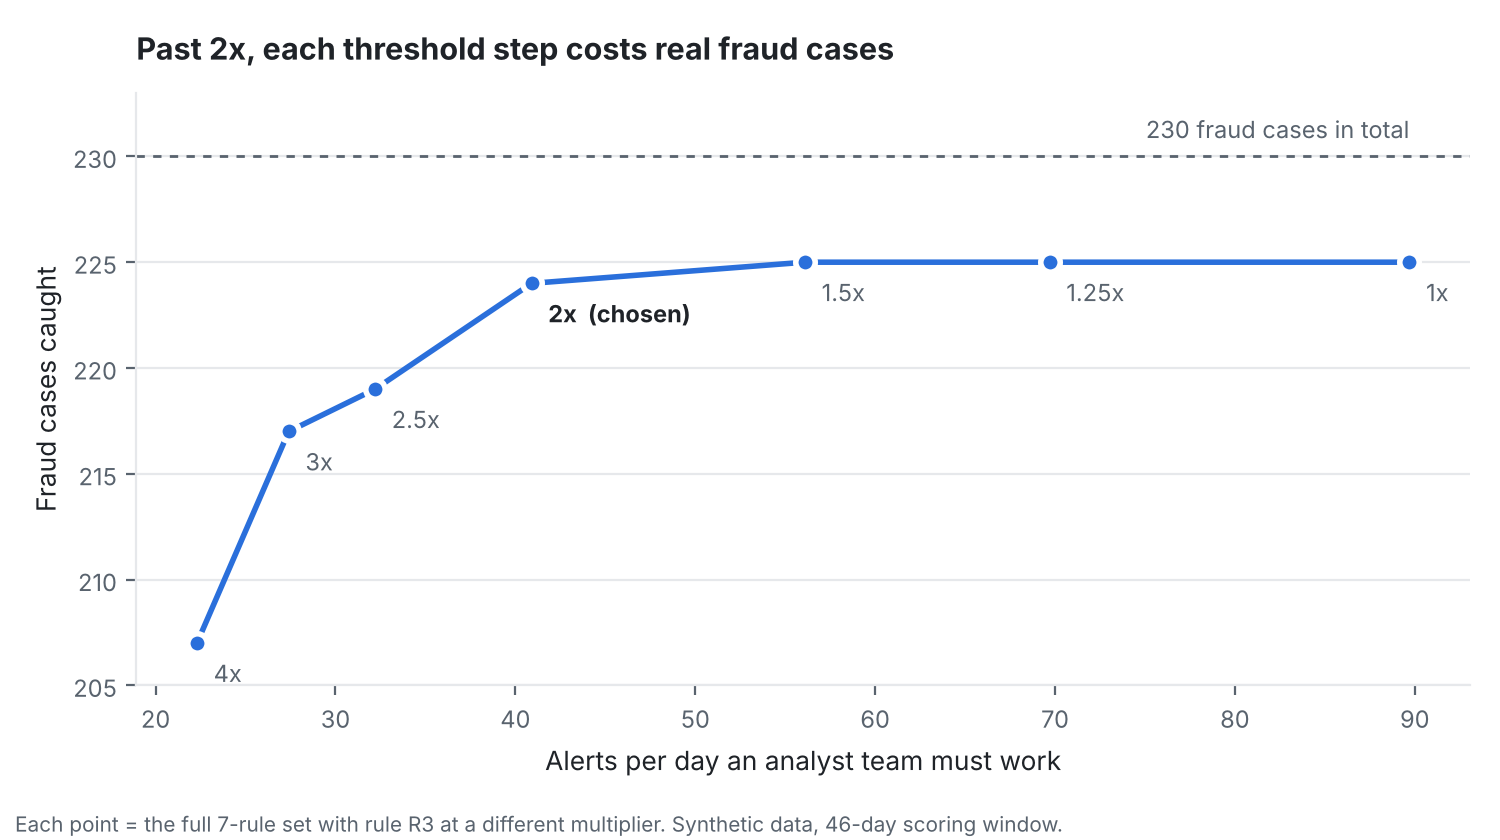
Seven SQL rules for account takeover, scams, card testing and money mules, scored against 585,000 labelled transactions. They catch 224 of 230 fraud cases at 41 alerts a day.
// detection · data · banking risk
I'm Shay Ramthol. I write SQL and Python detection rules, run security labs end to end, and spent years in bank lending and KYC/AML. That mix means I know how fraud and attacks get through, and how controls stop them.
// selected work
Each project shows the method and the numbers, including what didn't work.
Seven SQL rules for account takeover, scams, card testing and money mules, scored against 585,000 labelled transactions. They catch 224 of 230 fraud cases at 41 alerts a day.
All 22 EC-Council CCT lab modules completed. Ten exercises documented step by step and turned into a security and disaster recovery strategy for a research-vessel network.
Extracted admin credentials by hand with blind SQL injection, exploited stored XSS and IDOR flaws, and built an AES-CBC padding-oracle attack to crack the Encrypted Pastebin challenge. Earned private-program eligibility in September 2026.
A Python toolkit that pulls NZBN and Companies Office data, from the API and bulk files, into a local database with scheduled jobs. I designed the loaders so a thinner source file can never overwrite a richer existing record, which fixed a data-integrity bug found during the build.
// what I bring
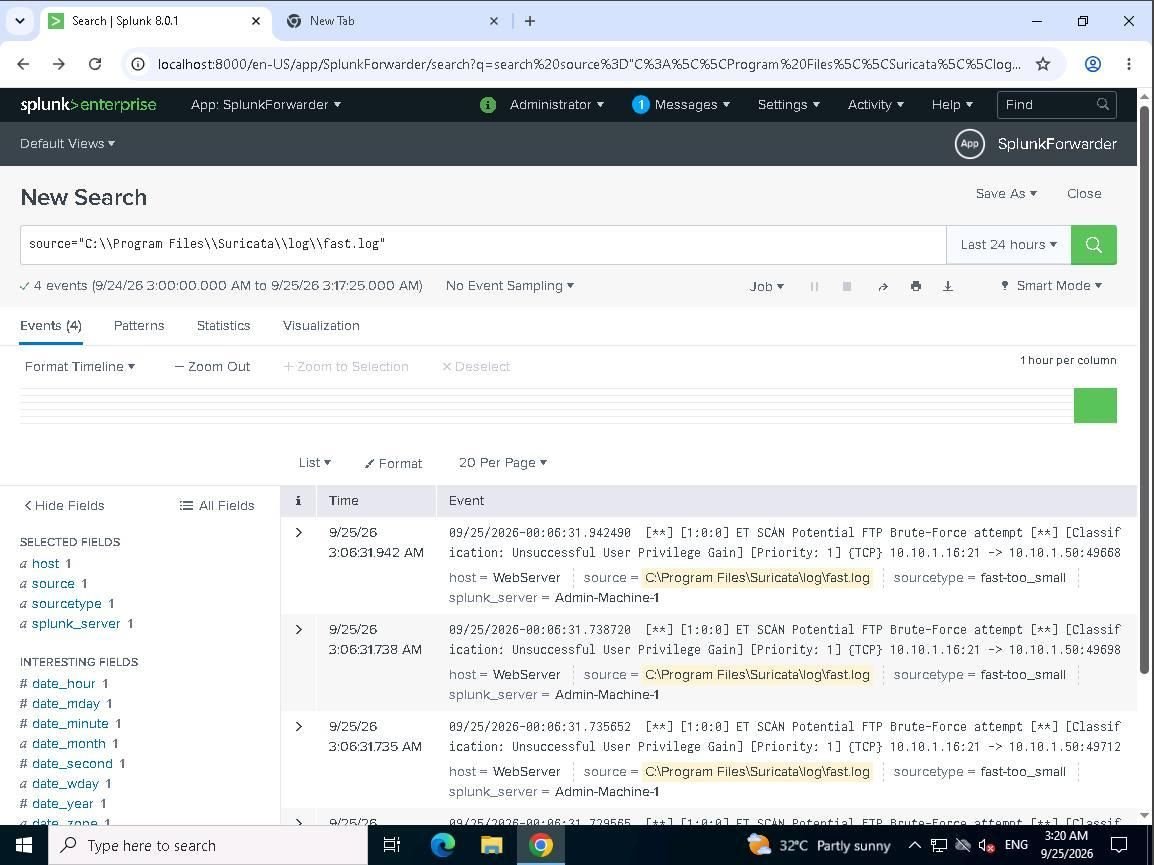
Fraud rules in SQL, Suricata IDS and iptables rules, alert review in Splunk. Tuned against real alert volume, not just accuracy.
SQL with window functions, Python pipelines and API integrations, RPA automation, and Excel models linking data across sheets and workbooks.
KYC/AML checks, credit assessment, loan validation and pre-funding verification at Bizcap; lending risk within delegated authority at BNZ.
Hack The Box CPTS path (in progress), Hacker101 CTF, NZ Cyber Security Challenge. Web, network and Active Directory testing.
Structured incident response, computer forensics, backup and restore, and continuity and disaster recovery planning.
Nearly a decade customer-facing in banking and B2B sales. I explain technical findings to the people who have to act on them.
// get in touch
I'm based in Auckland and open to roles in fraud detection, security operations and financial crime.